Data & privacyNote
Tinder fined €11m: its ‘Download My Data’ tool left data out
Ireland’s Data Protection Commission’s decision of 13 November: what Tinder’s data-download tool got wrong, what Article 15 of the GDPR entitles a user to, and an inquiry opened in 2020.

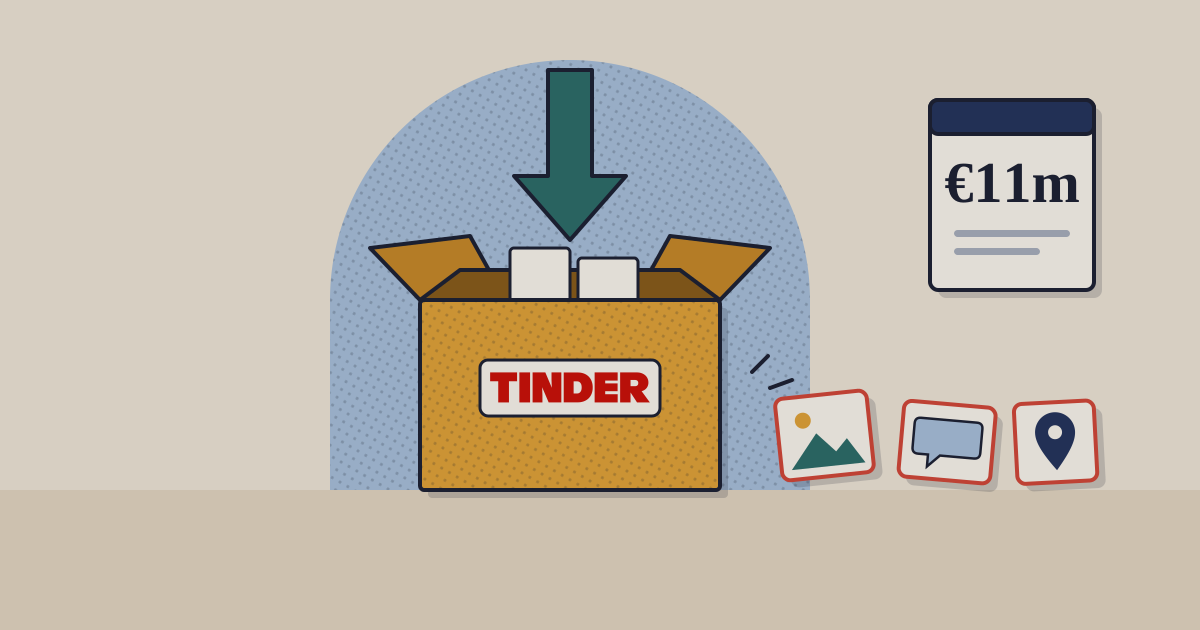
Ireland’s Data Protection Commission has fined MTCH Technology Services Limited, the company that runs Tinder in the EU, €11m and reprimanded it, because the app’s “Download My Data” tool did not give users a complete copy of their personal data. Some categories of information were left out without telling the user; others came only in summary form.1 The commission announced the decision on 13 November and ordered MTCH to bring its processing into line with the GDPR within three months. The inquiry behind it was opened in January 2020.1
€11m
fine, with a reprimand, on Tinder’s EU operator
DPC
Jan 2020
when the DPC opened the inquiry on its own initiative
DPC
3 months
to bring its processing into compliance
DPC
15(3)
the GDPR article on a copy of your data that the tool fell short of
DPC
01What the tool did wrong
The decision is about the right of access under Article 15(3) of the GDPR: a person who asks is entitled to a copy of the personal data a company holds on them. Tinder offered a self-service tool for that. The commission found that although the tool was presented as the way to get a copy of one’s Tinder data, it did not provide all of it, and what it did provide did not meet the requirements of the right of access.1 Deputy Commissioner Graham Doyle said “tens of thousands” of users used the tool during the period the inquiry assessed.1
These tools do not need to provide a complete copy of personal data but they must be fair and transparent to individuals regarding the extent of the data provided.
That is the point of the case: an export button may hand over less than everything, if it says so and tells the user how to get the rest. Tinder’s left categories out silently. The commission has not yet published the full decision, so which categories were missing is not public.1
The case started from complaints. On 4 February 2020 the commission said it had seen issues raised by people in Ireland and across the EU and would examine MTCH’s legal basis for processing, its transparency and how it handled requests from users exercising their rights.2 Its 2024 annual report described the inquiry as covering both access requests and erasure requests (Article 17), with MTCH replying to a preliminary draft decision that year.3 The 13 November announcement names only the access finding. As MTCH’s lead authority in the EU, the Irish commission decided the case with the cooperation of its peer regulators.1
02What Article 15 entitles you to
Under the GDPR, anyone can ask a company whether it holds personal data about them. If it does, they are entitled to:
- A copy of the data itself, the first one free; a reasonable fee is allowed only for further copies. A request made electronically gets an answer in a commonly used electronic form.4
- The facts around it: why the data is processed, which categories are held, who it has been or will be shared with, how long it will be kept, where it came from if not from the person, and whether automated decisions or profiling are used, with meaningful information about the logic involved.4
- An answer within one month, which the company may extend by two further months for complex or numerous requests, if it says so within the first month.4
The one limit in the article is that a copy must not adversely affect the rights and freedoms of others, such as another person’s messages.4
Europe is also writing new rules for how apps present choices to users: see our Analysis of the Digital Fairness Act proposal.
Sources
- Data Protection Commission, Data Protection Commission fines MTCH €11 million following Inquiry into Tinder users’ personal data requests — 13 November 2026
- Data Protection Commission, Data Protection Commission launches Statutory Inquiry into MTCH Technology Services Limited (Tinder) — 4 February 2020
- Data Protection Commission, Annual Report 2024, Decisions and Inquiries (p. 50) — June 2025
- Regulation (EU) 2016/679 (General Data Protection Regulation), Articles 12 and 15 — 27 April 2016
Disclosure. TechBag is a software reseller: it earns when companies buy through it, including from vendors named here. The analysis is TechBag’s own; no vendor paid for or saw this piece before publication. Facts are labelled reported, TechBag count or our view.
Keep reading